DevSecOps (Secure CI/CD)
DevSecOps Services: Secure CI/CD Pipelines for Faster, Safer Releases
Our DevSecOps services add security checks at every stage of your CI/CD pipeline to find vulnerabilities before they reach production.
Overview
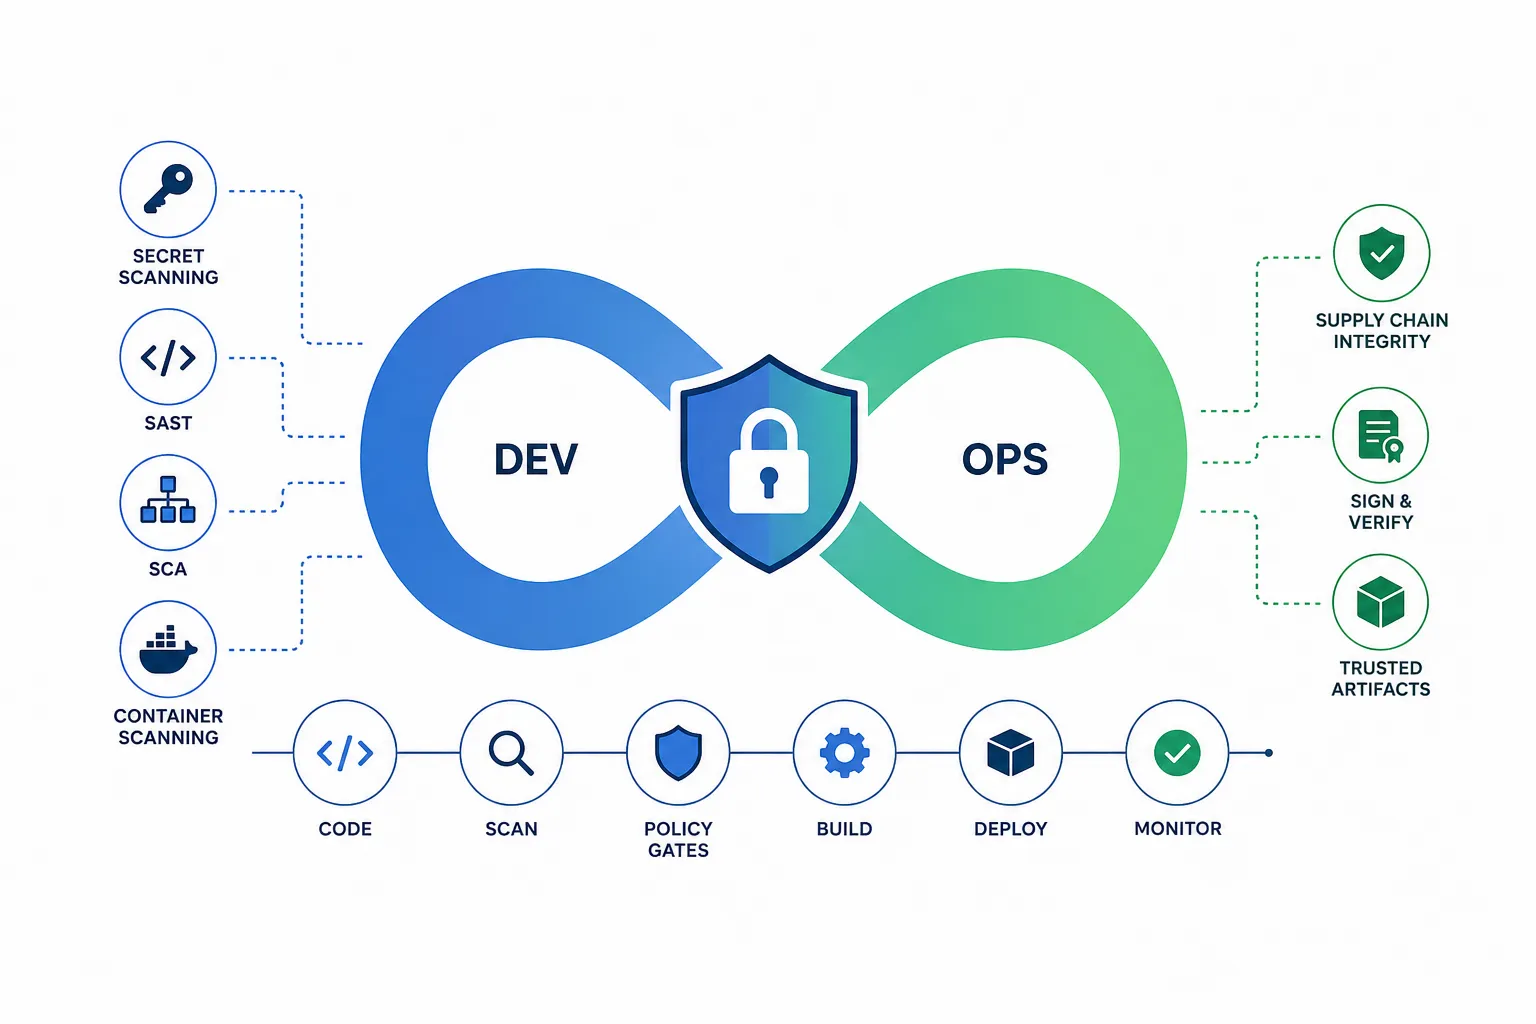
DevSecOps integrates security into your software delivery from the start rather than bolting it on at the end. We embed automated security testing into your pipelines, including secret scanning, SAST, software composition analysis and container scanning, add supply-chain integrity controls, and set policy gates so risky changes are caught early. Security becomes a shared, automated responsibility across development and operations. Embedding automated security and supply-chain controls throughout the pipeline reduces vulnerabilities reaching production and produces the auditable evidence needed for frameworks such as SOC 2, ISO 27001 and the EU CRA. Explore all Cloud & DevOps services, or read our DevSecOps guides on the blog.
Methodology & Standards
NIST Secure Software Development Framework (SSDF, SP 800-218), SLSA and sigstore for supply-chain integrity, the OWASP DevSecOps guidance, and pipeline-integrated SAST and SCA. Pairs with our secure code review and software composition analysis services. Security gates, signed artifacts and continuous policy validation are tracked as code, giving measurable, auditable assurance that controls remain effective as the pipeline evolves. For the cloud your pipeline deploys to, CSPMX, our cloud security posture management tool, flags misconfigurations continuously.
What's Included
What You Receive
Frequently Asked Questions
DevSecOps is the practice of embedding security in every aspect of the software development lifecycle, not as an afterthought but by design. Security checks are run on an ongoing basis inside your CI/CD pipeline, detecting vulnerabilities as soon as they enter the codebase. We'll help you establish automated security testing, secure CI/CD pipelines, container security, Infrastructure as Code (IaC) security and cloud-native application security.
Not if it is tuned. We tune your security scanners to eliminate false positives and focus only on the issues that require remediation. All scans run in parallel with caches to speed up the process, and results are available in your developers' tools of choice directly at the point of code submission.
DevSecOps is an embedded automated security testing solution that runs inside your DevOps pipeline. Secure code review brings manual code inspection to detect design and business logic problems that automated tools miss, including improper access controls. Software composition analysis (SCA) identifies open source components and their security risks, including supply chain attacks, and provides an SBOM (Software Bill of Materials). Used together, they provide broad and deep security testing that's fully automated and integrated into your DevOps workflow while still providing the precision of manual code reviews at critical points.
Automated scanning, SBOMs, signed artifacts and policy gates provide the evidence needed for SOC 2, ISO 27001 or EU Cyber Resilience Act (CRA) compliance. By being embedded in the development process, compliance is achieved as a natural consequence of the DevOps pipeline rather than as a separate and manual audit step.
Yes. We can add security stages to your existing GitHub Actions, GitLab CI or Jenkins pipelines. They are then tailored to your specific risk profile to provide maximum coverage and security without slowing down your development. Your teams can continue to follow exactly the same development and release processes as before, with security hardening applied as a natural part of the process. If you want us to operate the pipelines on your behalf as well, our managed DevOps service can do that too.