Threat Modeling
Threat Modeling Services for Secure-by-Design Systems
Identify security threats and architecture weaknesses early with expert threat modeling services using STRIDE, PASTA and secure design reviews.
Overview
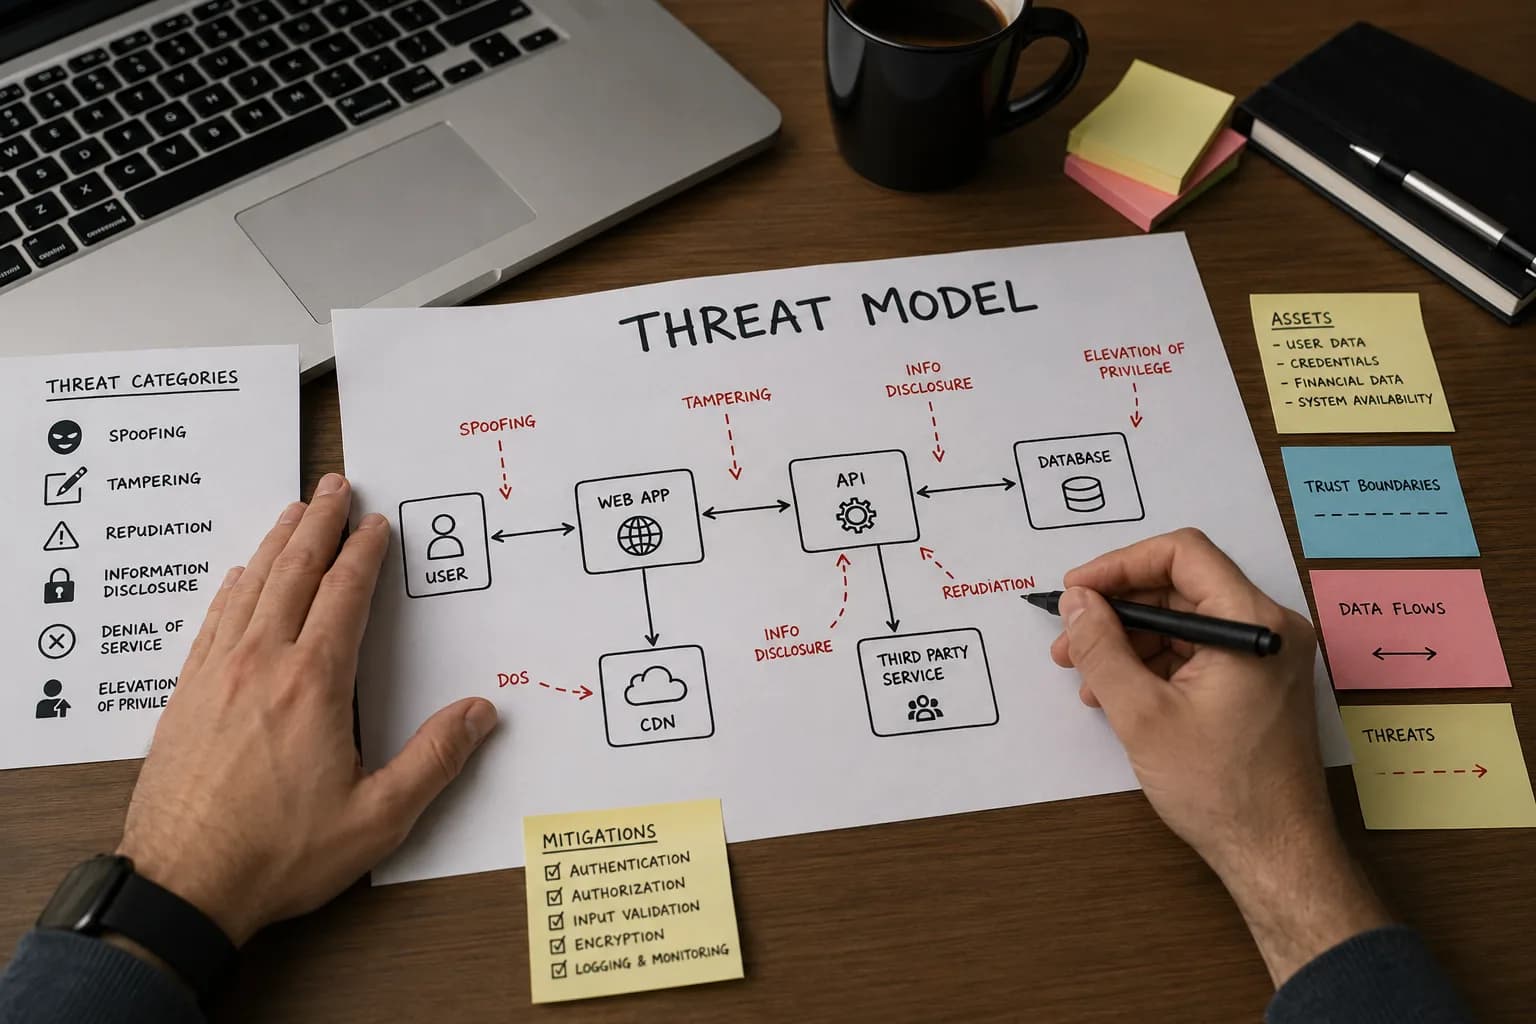
Threat modeling is a structured security assessment performed during the design and development stages to identify threats, attack paths and architecture weaknesses before they become vulnerabilities. It maps a system's architecture, data flows and trust boundaries, answering what can go wrong and what to do about it, so security weaknesses are discovered early, when they are cheapest to fix. Our threat modeling services use STRIDE, PASTA and secure design reviews to help organisations build secure-by-design applications and systems.
Methodology & Standards
Our threat modeling methodology uses STRIDE and PASTA, supported by attack trees, LINDDUN for privacy and the OWASP Threat Modeling Cheat Sheet. We define system scope, map data flows and trust boundaries, identify threats and attack paths, assess impact, and prioritise risks with actionable mitigation guidance.
What's Included
What You Receive
Frequently Asked Questions
As early as possible, at design or major-redesign stage, before code is written. That is when you can change architecture cheaply, and it tells pentesters where the real risk concentrations are.
We pick the fit. STRIDE is fast and systematic for per-component enumeration; PASTA is risk- and business-centric for higher-stakes systems. We often combine them and add LINDDUN for privacy.
Threat modeling is typically performed during the design phase of the Software Development Life Cycle (SDLC) to identify security risks before development begins, reducing remediation costs and improving security by design.